Among the most targeted networks
Government systems are a standing target for nation-state actors. The servers that run public services carry a power layer below the operating system, the part few tools watch.
 BareketAI PWXRequest a pilot
PWX brings security to the power layer of government infrastructure, the control chips beneath every server in your data centers and agency networks, the layer most security tools cannot see. Running as software on the fleet you already have, it maps the power chips across every site, watches how they behave in real time, and gives each event a clear verdict: normal, suspicious or attack.
Request a pilotGovernment agencies run essential services on fleets of servers across data centers and agency networks, and they sit among the most targeted organizations in the world. Every one of those servers relies on power control chips, managed through the BMC, that sit below the operating system and outside the view of most security tools. That makes the power layer a growing target for a sector that answers to strict mandates: state actors reach government systems through the supply chain, attackers exploit server management chips, and idle compute is hijacked for hidden crypto mining. PWX brings visibility and fast detection to this layer, running as software on the fleet you already have and sending clear verdicts into the SOC tools you already use.
Government systems are a standing target for nation-state actors. The servers that run public services carry a power layer below the operating system, the part few tools watch.
Attackers already exploit server management chips, and researchers have shown that one command through them can bend a server's power to disrupt service or damage hardware.
Idle capacity across agency data centers is a quiet target for crypto miners that hide from monitoring tools. The power they draw is harder to hide.
Agentless. Finds every power component across the fleet, maps firmware to known CVEs and shows attack paths from an exposed BMC to GPU damage.
Continuous monitoring, alerts and SIEM export into Splunk or Datadog.
Modules for millisecond detection by the PWX-01 agent on the BMC, up to PWX-06 inline blocking (roadmap).
Every verdict is recorded and summarized in regular reports your team can use as evidence for NIST 800-53, FISMA and internal audits across your estate.
PWX deploys as software across the existing fleet, from one site to thousands, with no new chips and no board redesign.
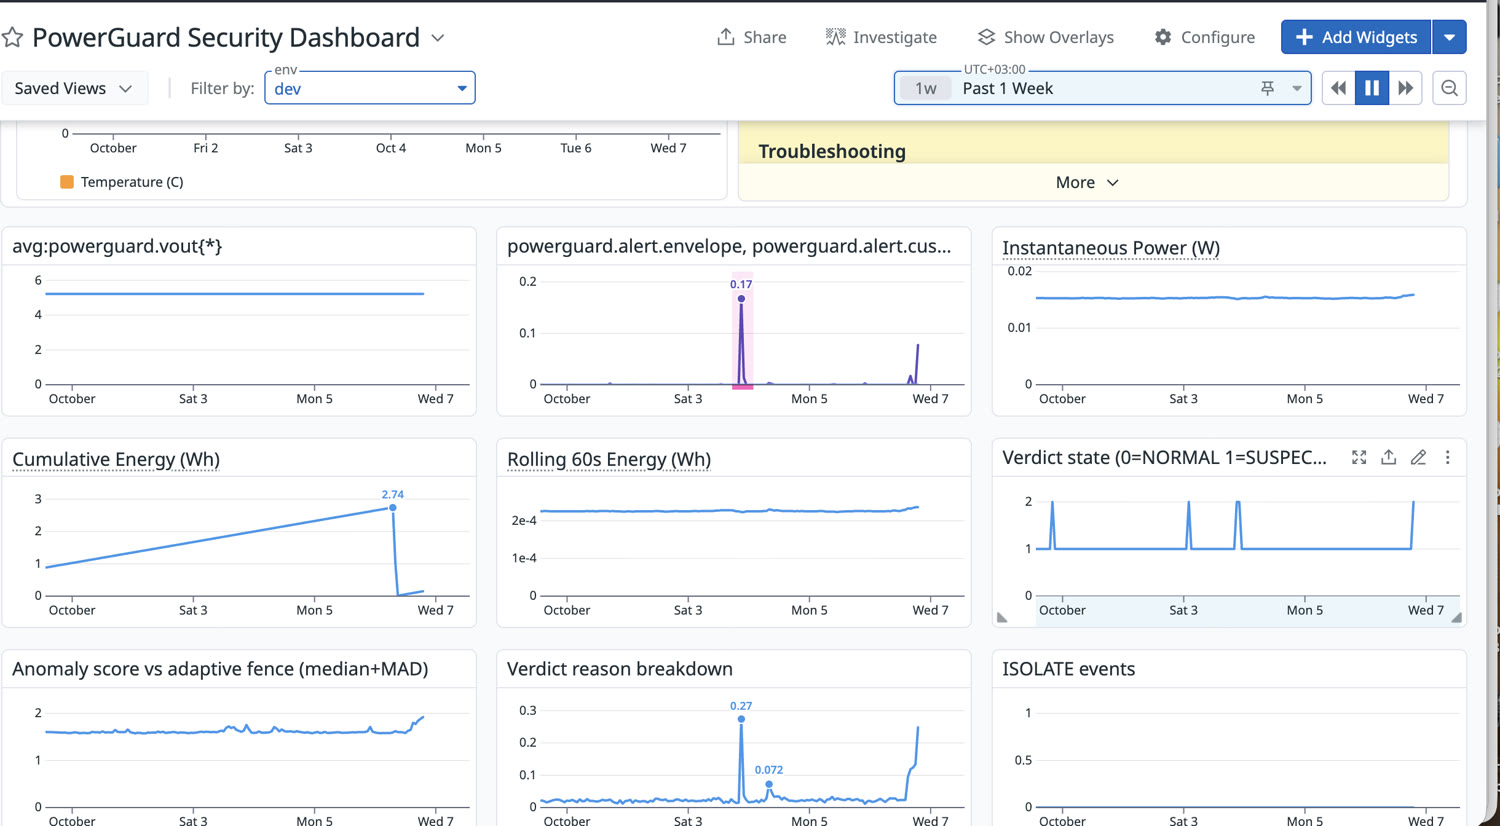
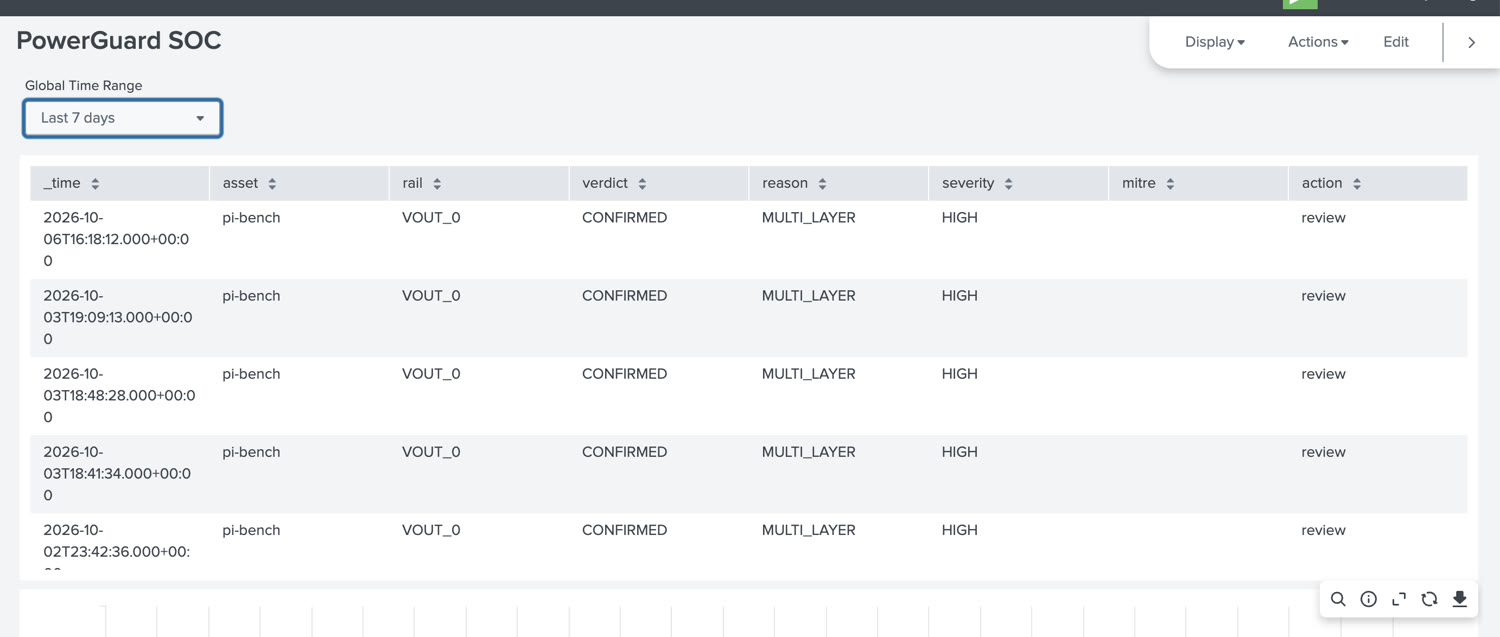
Not a mockup. A live voltage attack pulled a rail from 5.21 V to 4.64 V and was detected in about 20 ms, streamed into Datadog and Splunk, the same tools your team already lives in.
CISA directed federal agencies to mitigate the SolarWinds Orion compromise after a state actor reached government networks through trusted software.
Read moreNIST · SP 800-53NIST SP 800-53 defines the security and privacy controls that federal information systems are measured against.
Read moreCISA · JUNE 2025A server management chip flaw (CVE-2024-54085) was added to CISA's Known Exploited Vulnerabilities catalog.
Read moreAWS SECURITY BLOG · NOV 2025A cryptomining campaign deployed miners on Amazon EC2 and ECS within ten minutes of gaining access.
Read more