PWX Discover
Agentless. Finds every power component across the fleet, maps firmware to known CVEs and shows attack paths from an exposed BMC to GPU damage.
Open the live console BareketAI PWXRequest a pilot
A compromised administrator or firmware component can issue commands beneath SIEM and EDR visibility. PWX maps this hidden layer, establishes a physical baseline and raises a verdict from the rail before hardware is damaged.
Agentless. Finds every power component across the fleet, maps firmware to known CVEs and shows attack paths from an exposed BMC to GPU damage.
Open the live consoleContinuous monitoring, alerts and SIEM export, into the tools you already run.
See the integrationsSix modules, from millisecond detection by the PWX-01 agent on the BMC to inline blocking with PWX-06. PWX-01 is proven on our bench; PWX-06 is on the roadmap.
See the six modulesPWX Discover, agentless, to see the fleet through Redfish. The PWX-01 agentwhere you need milliseconds, on PMBus. Every power event is tied to who issued it, what hit the rail and what it did to the CPU and GPU, then correlated at the edge into one verdict.
What Dana, Alex and Finkel open every morning: the fleet without an agent, the paths to the power, the rail live at 100 Hz, the findings that reach the SOC, and how an attack is stopped and proven.
Power surface: every way in to the power →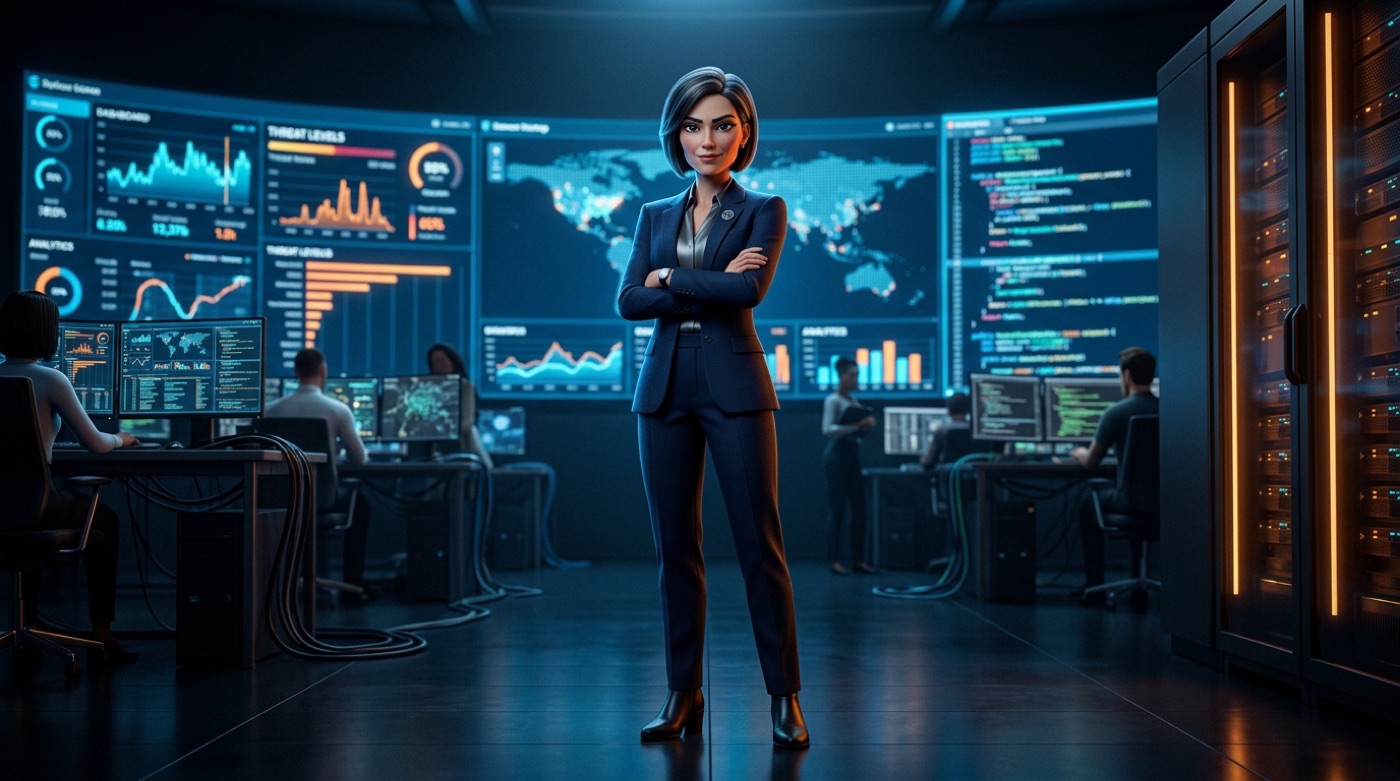 DANA · SOC LEADPILOT
Every setting that lets a host reach a rail, scored across every vendor and re-checked every four hours. Dana fixes the one that protects the most hardware first.
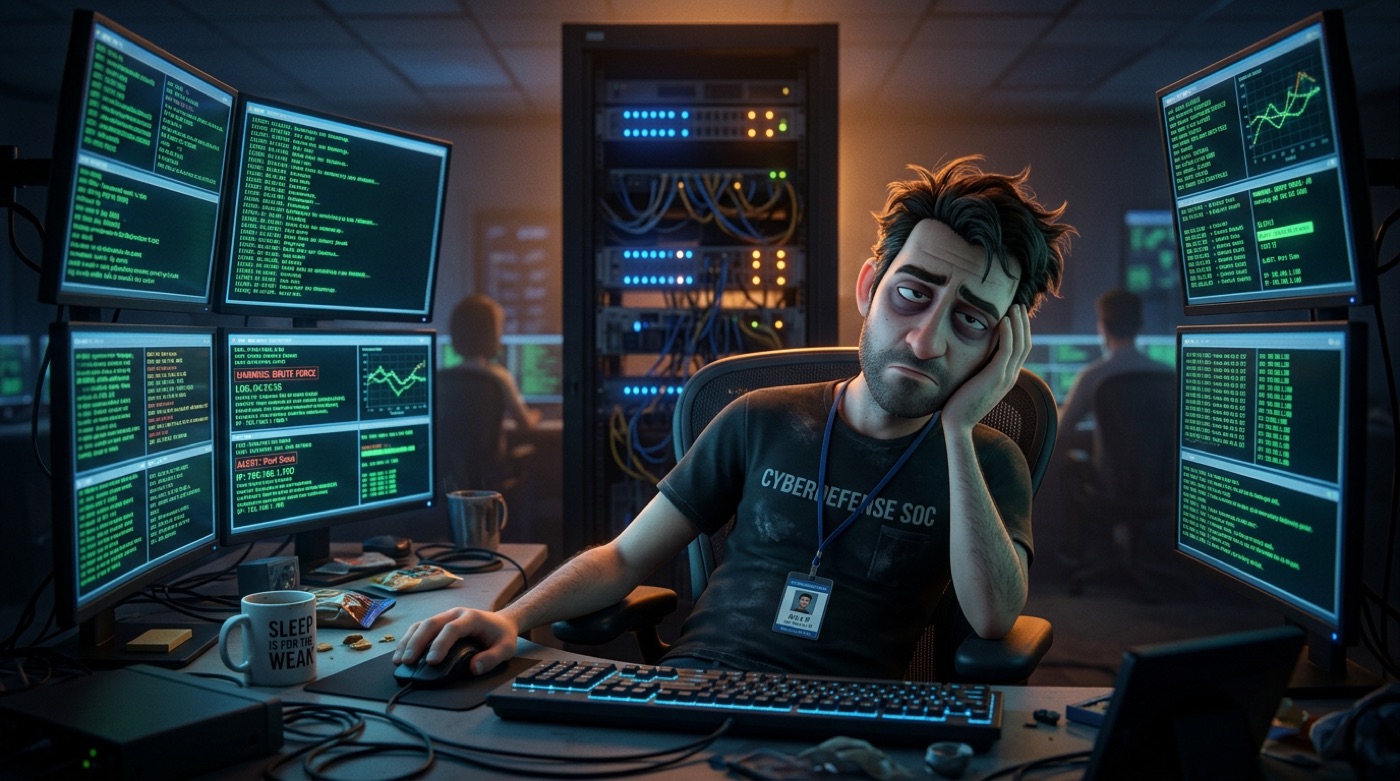 ALEX · SOC ANALYSTTODAY
A hundred samples a second from the regulator. When a command drives the rail outside its safe range, the verdict strikes with the physical evidence attached, then the rail settles. Alex gets the finding, not the firehose.
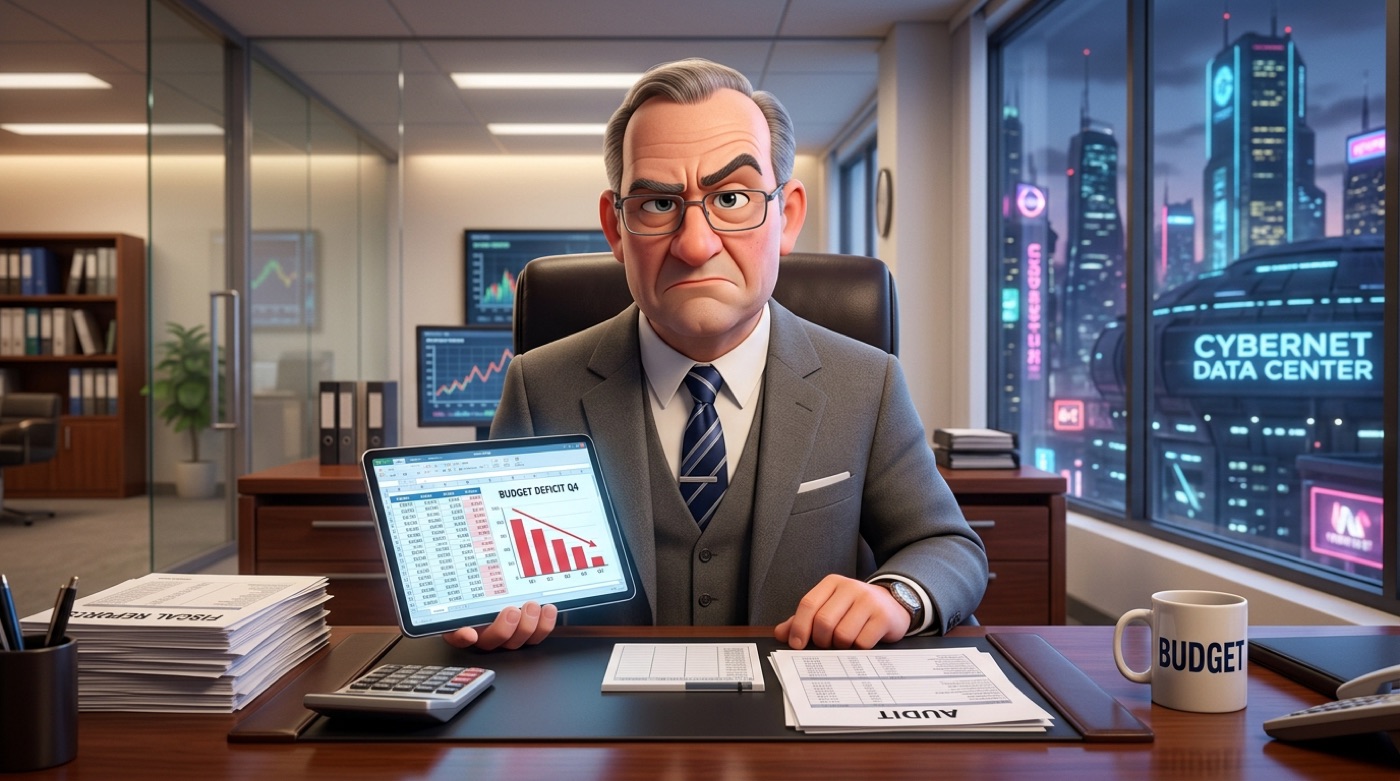 FINKEL · CFOPILOT
Read-only through the management interfaces the fleet already has. Model, firmware and source for every BMC, regulator, GPU board and PDU. Nothing new in the rack, nothing to approve.
| Layer | Asset | Model | Firmware | Source |
|---|---|---|---|---|
| BMC | gpu-node-17 | Dell iDRAC9 | 7.10.50 | Redfish |
| Regulator | CPU0 VCORE | Infineon XDPE | rev 2A | Redfish * |
| GPU board | HGX · 8× H100 | NVIDIA HGX | 24.03 | HMC |
| PSU | PSU 1 | Delta 3,200 W | 00.0E.02 | Redfish |
| Rack power | R12 · PDU A | Raritan PX4 | 4.2.0 | SNMP |
Read-only through Redfish, IPMI, DCGM and SNMP. Model, firmware and source for every BMC, regulator, GPU and PDU. Nothing installed, no new hardware.
The settings an attacker needs to reach the power: BMC accounts, the host-to-BMC channel, firmware age, rail write-protection. Drift shows up before an attacker uses it.
PWX follows each path from a host through the BMC to the regulator and the GPUs behind it, and ranks it by the hardware it can physically break.
The agent reads every regulator rail a hundred times a second. When a command drives a rail outside its safe range, the verdict lands in 20 ms with the physical evidence attached.
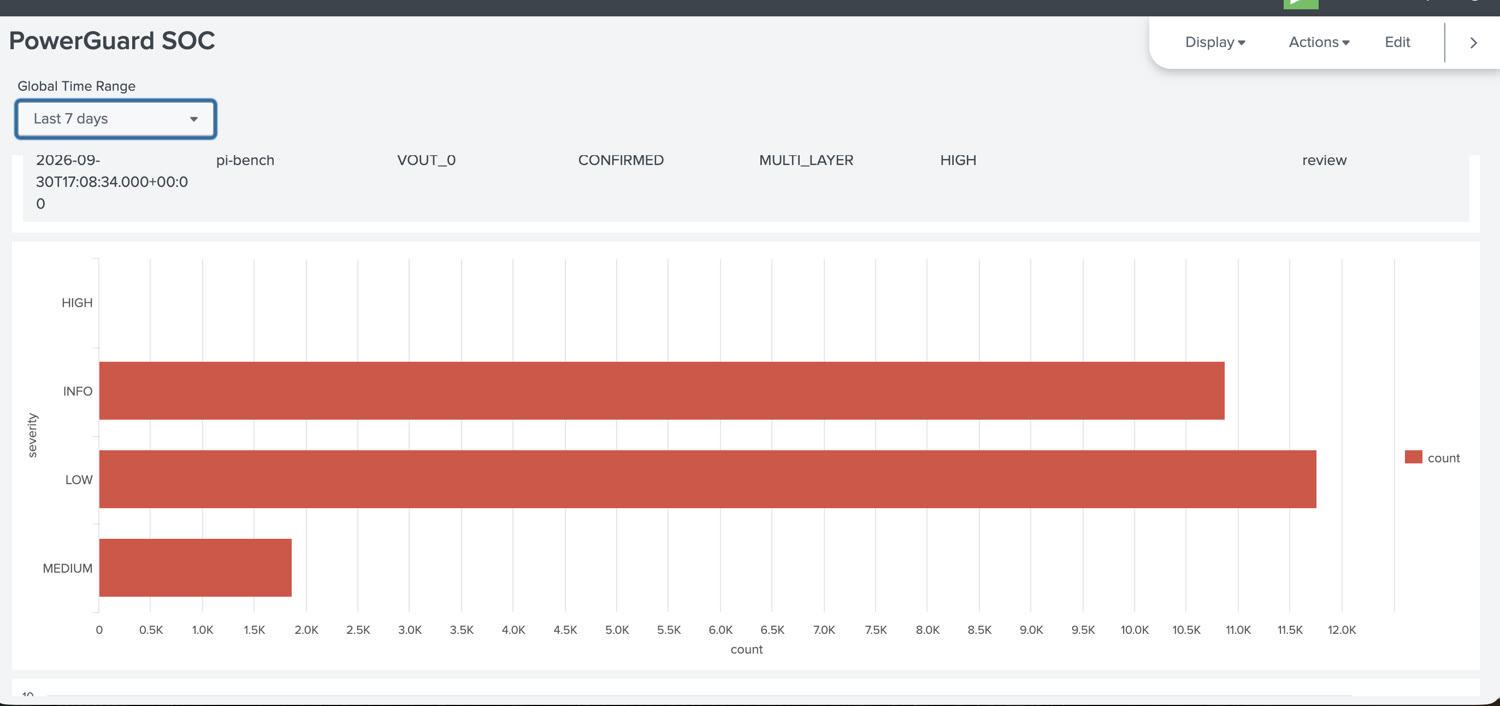
Forty thousand power events become three findings, each with the asset, the evidence and the ATT&CK mapping, in the Splunk or Datadog your team already runs.
The same 100 Hz stream scores the health of every rail: ripple, drift and thermal margin. Failing regulators show up days ahead, so the fleet runs closer to its real limits.
When an attack is live there is no time for a ticket. PWX-06 filters power commands inside the BMC and drops a malicious write before it reaches the rail. Detection at the rail runs today.
Who issued the command, what it did to the rail, what PWX decided and what your controls did, in one signed record. The same record feeds the NIS2 and IEC 62443 evidence packs.
The agent on the BMC: rails sampled at 100 Hz, attack to verdict in milliseconds
PWX-02 · NEXTAgent-grade evidence for NIS2 and IEC 62443, with evidence packs on demand
PWX-03 · NEXTDegrading power hardware surfaced before it takes a server down
PWX-04 · ROADMAPCertification for the vendors who build the power components, against the standard your fleet is measured by
PWX-05 · ROADMAPAgent verdicts carried into your OT and security tools, beyond the SIEM export in PWX Monitor
PWX-06 · ROADMAPEvery power command checked against policy inside the BMC; a malicious write dropped before it reaches the rail
An attacker who reaches the power layer can damage silicon permanently, and nothing above it will record how. PWX holds a physical baseline of your hardware and acts on physical evidence, not on a statistical guess.
The same measurements show hardware degrading before it fails. Power components drift for hours or days before they take a server down.
Early-warning capability is being validated with design partners on production hardware.
Attacks beneath EDR don't write logs. I need evidence, not a guess.Physical evidence in 20 ms.
Ten thousand alerts a day. I need the three that matter.Findings, not firehose.
Not one dollar of new hardware.Nothing installed to start. No new silicon.
You cannot audit a component by asking it how it is doing.
Every server in your estate contains a management controller running firmware you did not write and cannot inspect. It has authority over the physical power of the machine. PWX gives you an independent view of what that layer is actually doing, and a switch that belongs to you.
Every controller ships with code authored under someone else's jurisdiction
We observe the power layer rather than trusting what it reports about itself
Runs fully inside your environment, including disconnected networks
No workload content, no customer data, ever
Enforcement acts under policy you set and can revoke
Designed for defence, government and national infrastructure environments.
On sovereignty and enforcement leverage · Stefan Fritz →
Findings delivered into the tools you already run, see the live Datadog stream on Proof.
The power layer is inside the scope of the major OT and infrastructure frameworks, and today it is the part of the estate with the least evidence behind it. PWX is designed to produce that evidence, on demand.
| FRAMEWORK | OBLIGATION AREA | WHAT PWX PRODUCES |
|---|---|---|
| NIS2EU 2022/2555 · ART. 21 | Risk-management measures: asset visibility, incident detection and handling, evidence for reporting | Continuous inventory of the power layer; detection with a physical evidence trail; an incident record that survives the incident |
| IEC 62443INDUSTRIAL AUTOMATION & CONTROL | Continuous monitoring and asset inventory of control systems | Per-controller monitoring against a baseline learned from your own hardware; evidence packs on demand |
| NERC CIPBULK ELECTRIC SYSTEM | System security management and internal network security monitoring for cyber systems | Behavioural monitoring of the management plane; alerting into your existing tools; retained records under your control |
PWX PRODUCES EVIDENCE. COMPLIANCE ITSELF REMAINS AN ASSESSMENT OF YOUR WHOLE ENVIRONMENT · NO SINGLE PRODUCT MAKES YOU COMPLIANT, AND WE DO NOT CLAIM OTHERWISE.